Table of Contents
-
How To Choose Managed Services Provider For Regulated Operations
-
How To Choose Managed Security Services Without Buying Disconnected Tools
-
Managed Services Selection Criteria That Protect Budget And Workflow
-
Managed Services Vendor Selection Criteria For Cloud And Endpoint Control
-
Questions To Ask During MSP Discovery So Scope Does Not Drift
-
Choose A Provider That Is Security Ready And Compliance Ready
Access approvals are waiting, laptops are creating repeat tickets, M365 requests are piling up, and compliance evidence is missing right when leadership needs it for a client, auditor, or insurer. That’s why choosing a managed services provider and how to choose managed security services are operational questions, not shopping exercises.
A recent study found 60% named cybersecurity as the top challenge leading them to work with an MSP. Cyber Security Solutions supports Managed Cloud Services and fully managed IT under a single contract, tying operations, security, compliance, hardware lifecycle, M365 administration, and incident response to one accountable workflow.
Robert Langley, VP of Compliance at Cyber Security Solutions, notes: “Start with the work people need done every week, then confirm who owns each ticket, control, log, device, approval, and evidence record.”
How To Choose Managed Services Provider For Regulated Operations
Tickets need answers, devices age, invoices arrive, and audit evidence has to be ready on request. The first evaluation should reduce daily friction while protecting budget, evidence, and client data. About 55% of companies approach MSPs for value-added services and reduced security risks, but value depends on scope clarity.
-
Scope before tools: Define covered users, devices, systems, and data before pricing.
-
Support meets compliance: Keep help desk, endpoint management, cloud administration, and evidence collection connected.
-
Pricing is explainable: Ask what is included, excluded, and billable as an add-on.
-
Ownership is visible: Confirm who monitors endpoints, reviews logs, updates policies, and documents incidents.
How To Choose Managed Security Services Without Buying Disconnected Tools
Security value comes from operated controls, not product names. Businesses know this, with 44% specifically seeking MSPs for cybersecurity capabilities. As both an MSP and MSSP, Cyber Security Solutions looks for endpoint protection, access controls, MFA, audit logging, incident response documentation, and role-based training that someone runs, reviews, and documents.
A user clicks a suspicious tax season email, an endpoint alert fires, MFA blocks a login attempt, logs are retained, and incident notes are ready for management review.
Evaluate endpoint monitoring, identity controls, cloud administration, and incident documentation together.
Managed Services Selection Criteria That Protect Budget And Workflow
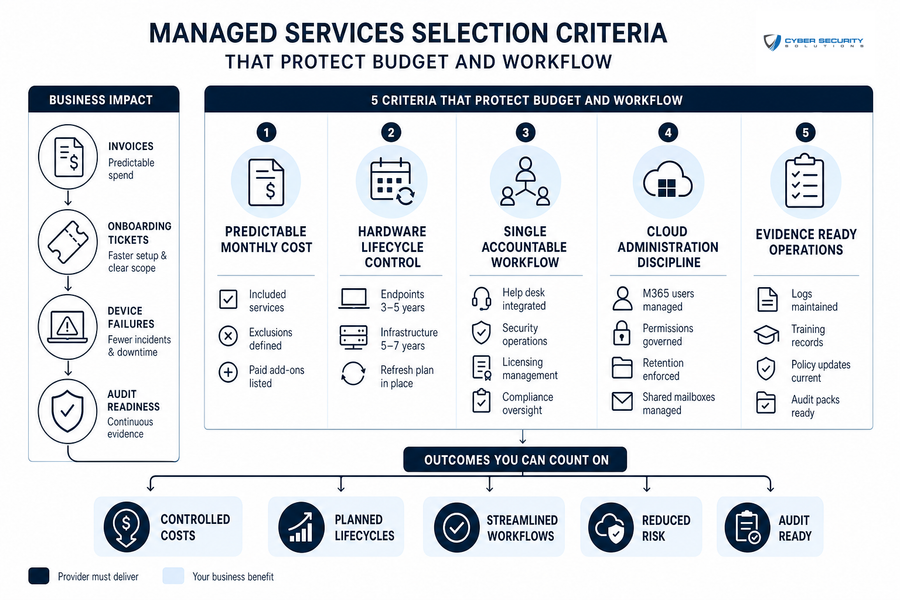
Your managed services selection criteria should connect to invoices, onboarding tickets, device failures, and audit readiness, especially when 47% of MSPs say current project practices damage profitability. Require the same clarity Cyber Security Solutions builds into managed tiers above Micro: security and compliance defined up front, with documented inclusions, exclusions, and paid add-ons.
-
Predictable monthly cost: Document included services, exclusions, and add-ons before signing.
-
Hardware lifecycle control: Plan endpoint refreshes every 3 to 5 years and infrastructure every 5 to 7 years.
-
Single accountable workflow: Tie help desk, security operations, licensing, and compliance together.
-
Cloud administration discipline: Include M365 users, permissions, retention, shared mailboxes, and role changes.
-
Evidence-ready operations: Maintain logs, training records, and policy updates continuously.
Related Managed Services Guidance
MSP Qualifying Questions For Compliance-Bound Businesses
The right MSP qualifying questions reduce ambiguity before the agreement is signed, especially when 74% of organizations say security skill gaps negatively affect objectives. Use frameworks such as HIPAA 45 CFR 164.308(a)(8), ABA Model Rule 1.1, IRS Publication 4557, GLBA, the FTC Safeguards Rule, SEC, FINRA, and PCI DSS to clarify evidence, scope, confidentiality duties, client data handling, and accountability.
-
Which obligations, systems, users, locations, and records are in scope or excluded?
-
Who writes, maintains, and maps policies to operating controls?
-
How is incident response documented, tested, and escalated?
-
How are audit logs reviewed, retained, and reported?
-
How is staff training assigned, tracked, and refreshed by role?
Managed Services Vendor Selection Criteria For Cloud And Endpoint Control
Cloud systems and endpoints are where work gets done, from client files to appointment systems to M365 mailboxes.
Since 39% of MSPs report major setbacks adapting to advanced security technologies, managed services vendor selection criteria should test operating maturity, not tool familiarity.
-
User lifecycle management: Confirm onboarding, role changes, and offboarding follow documented approvals.
-
Endpoint monitoring coverage: Confirm devices are configured, patched, monitored, and documented.
-
M365 administration control: Confirm permissions, shared mailboxes, MFA, and licensing are actively managed.
-
Cloud service accountability: Confirm Managed Cloud Services support is included in the operating model, not passed between vendors.
These checks make accountability visible before cloud and endpoint gaps become daily friction.
Questions To Ask IT MSP Before Signing The Agreement
Changing providers, adding security oversight, or formalizing compliance workflows can disrupt staff who already have tickets waiting.
Since B2B buyers spend 83% of their journey researching independently, use these questions to ask IT MSP candidates before signing.
-
Inventory users, devices, locations, applications, cloud services, and sensitive data types.
-
Request a written scope with included systems, excluded systems, and paid add-ons.
-
Review service levels, escalation paths, exit provisions, and hardware ownership.
-
Ask for sample reporting on tickets, alerts, patch status, training, and evidence.
-
Confirm how the provider works with existing IT staff or vendors.
Choose an MSP Built for Security
Align support, cloud, endpoints, and compliance evidence under one accountable workflow with Cyber Security Solutions.
Questions To Ask An MSP About Accountability On Day One
Day one is where the agreement becomes real: tickets arrive, access requests wait, laptops need setup, and alerts need review. With 90% of MSPs reporting at least one cybersecurity incident in the past year, use questions to ask an MSP about accountability before work begins.
-
Ticket ownership and escalation: Define who owns each ticket and how handoffs are documented.
-
Access approval workflow: Clarify who approves access, role changes, and privileged permissions.
-
Device and software control: Assign procurement, setup, patching, replacement, and licensing.
-
Security exception documentation: Record risks, exceptions, and workarounds until closure.
Questions To Ask During MSP Discovery So Scope Does Not Drift
Scope must come before pricing because missed systems turn into inflated proposals, unmanaged obligations, and audit confusion. Moovila found 47% of MSPs believe project practices damage profitability, with scope creep and bad timelines cited. Use questions to ask during MSP discovery so controls align to the real operating environment.
-
Map the environment: Identify devices, users, cloud platforms, vendors, networks, and data flows.
-
Define the boundary: Separate in-scope assets from excluded assets and document why.
-
Match controls to duties: Connect safeguards to compliance, contracts, insurance, and business needs.
-
Package evidence early: Identify needed logs, policies, reports, training records, access documentation, and incident materials.
Choose A Provider That Is Security Ready And Compliance Ready
The right MSP/MSSP relationship should make daily operations clearer before it makes them more complex. Look for clear scope, operated security controls, cloud and endpoint accountability, compliance evidence, transparent inclusions and exclusions, collaborative transition planning, and exit provisions.
At Cyber Security Solutions, managed IT, managed security, and compliance support come together in one accountable model, from help desk tickets and M365 administration to endpoint monitoring, audit logs, and incident response documentation. Security Ready. Compliance Ready. Always Ready.
Start with a scoped discovery conversation, not a pressure-based replacement pitch, and turn waiting access approvals, repeat device tickets, and missing evidence records into an accountable Monday-morning workflow.