Table of Contents
Orlando technology decisions show up in ordinary work before they show up in board reports: client files in cloud apps, CUI in project folders, invoices awaiting approval, patient records in scheduling systems, help desk tickets, remote access, and vendor workflows.
Robert Langley, VP of Compliance at Cyber Security Solutions, notes: “Start with the workflows that move money, regulated data, and approvals, then assign ownership, evidence, and response steps before buying another tool.”
That’s why top Orlando tech companies treat cybersecurity as an operating discipline, not a side project. Cybersecurity Ventures reports cybercrime costs could top $10.5 trillion this year, but the local issue is simpler: can your team keep working, prove control, and protect the data clients trust you to handle?
How Top Orlando Tech Companies Turn Cyber Risk Into Operating Discipline
Generic advice breaks down when teams touch client records, controlled data, cloud apps, vendor portals, remote approvals, and billing workflows every day. With 81% rating cybersecurity as a high priority and 68% rating their organization as highly capable, top tech companies in Orlando still need practical ownership, not tool collecting.
-
Executive control ownership: Leaders assign decisions, budgets, and exceptions so approvals do not stall.
-
Access reviewed often: MFA, role-based access, and login audits protect shared portals and reduce vendor friction.
-
Endpoints actively monitored: EDR/XDR and SOC review help contain issues before tickets pile up.
-
Evidence stays current: Response procedures, POA&M updates, and records make audits cleaner.
What Top Tech Companies In Orlando Are Watching At Major Cybersecurity Events
Conference attendance creates value only when ideas become ownership, budget decisions, evidence, and operating changes. Since 85% of organizations increased their cybersecurity budget in 2024, large tech companies in Orlando should treat events as planning inputs for access reviews, response testing, compliance evidence, and renewal decisions.
|
Event |
Security Focus |
Business Takeaway |
Operational Follow Through |
|---|---|---|---|
|
InfoSec World 2026 at Gaylord Palms Resort & Convention Center |
Security leadership and risk |
Prioritize controls tied to data access |
Assign owners and evidence due dates |
|
Gartner IT Symposium/Xpo 2026 at Walt Disney World Resort |
IT strategy and investment |
Connect security spend to approvals and service uptime |
Update roadmap and renewal calendar |
|
9th Annual Summit on Security & Third-Party Risk at Loews Sapphire Falls Resort at Universal Orlando |
Vendor risk |
Tighten portal and supplier access |
Review vendor roles quarterly |
|
CyberDefenseCon 2026 at The Ritz-Carlton, Orlando |
Defense operations |
Improve detection and response planning |
Test escalation paths and logs |
Where Large Tech Companies In Orlando Focus First
Mature programs start with operational choke points, not another round of disconnected tools. The largest tech companies in Orlando focus first on controls that keep approvals moving, client files protected, vendor portals governed, remote access accountable, and regulated data supported by evidence.
-
Identity and MFA coverage: Tie approvals, payroll, and vendor portals to role-based access and MFA. Document exceptions so help desk tickets don’t become informal access approvals.
-
Endpoint detection and response: Monitor laptops, servers, and mobile devices, especially for remote staff. EDR/XDR coverage matters most when a compromised device can reach client records, invoices, or project files.
-
Secure remote access paths: Align VPN and secure gateway rules with who needs access, from where, and why.
-
Vendor risk and portals: Review third-party access to invoices, tickets, regulated data handoffs, and shared cloud folders. Vendor access needs an owner, expiration date, and review cadence.
-
Incident response evidence: If CUI is involved, NIST SP 800-171 expects documented response activity. Preserve logs, tickets, decisions, and POA&M updates.
Keep Building Cybersecurity Discipline
Why Largest Tech Companies In Orlando Treat Compliance As Proof Of Control
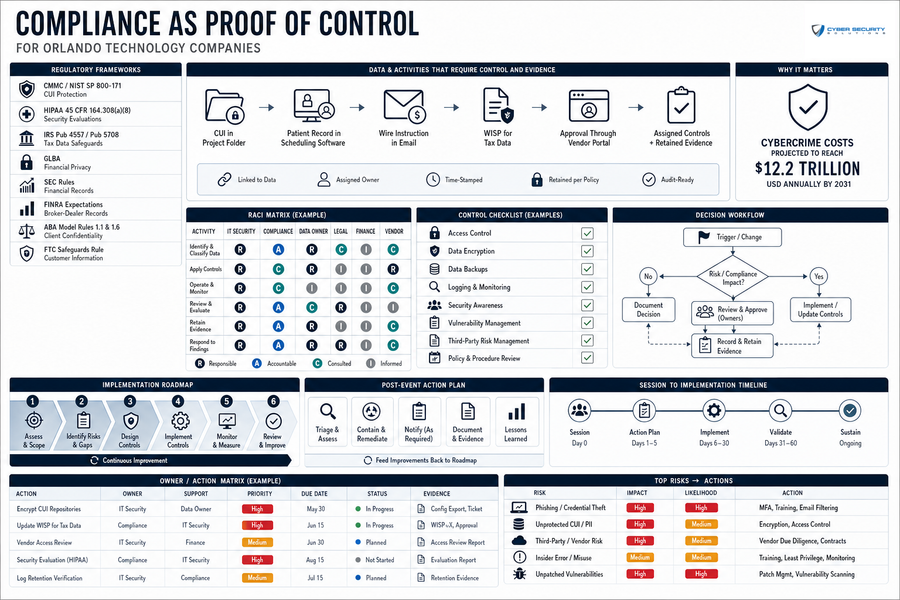
Compliance is useful when it proves work is being done, reviewed, and documented. For Orlando technology companies, that proof depends on the data and the obligation attached to it: CMMC and NIST SP 800-171 for CUI, HIPAA 45 CFR 164.308(a)(8) for security evaluations, IRS Pub 4557 and IRS Pub 5708 for tax data safeguards and WISP requirements, GLBA, SEC rules, FINRA expectations, ABA Model Rules 1.1 and 1.6 for competence and confidentiality, and the FTC Safeguards Rule for customer information.
That means CUI in a project folder, a patient record in scheduling software, a wire instruction in email, a WISP for tax data, and an approval through a vendor portal all need assigned controls, documented review, and retained evidence.
Cybercrime costs are projected to reach $12.2 trillion USD annually by 2031, so documentation can’t sit apart from operations. It has to reflect the work.
How Orlando Technology Companies Make Security Measurable
Leadership should track whether controls are working through evidence,Improving security and privacy is a top IT priority for many organizations.
Good measurement shows up in ordinary artifacts: MFA enrollment, endpoint coverage, patch status, phishing training completion, blocked risky sign-ins, incident response logs, vendor access reviews, POA&M updates, SSP documentation, and compliance dashboard reporting. Those records give leaders a clearer basis for decisions than memory or informal status updates.
For big tech companies in Orlando handling regulated work, continuous evidence collection turns CMMC and NIST SP 800-171 readiness into a repeatable operating habit.
Make Cybersecurity a Daily Discipline
Turn Orlando tech workflows, access, and compliance evidence into repeatable controls with Cyber Security Solutions.
What Big Tech Companies In Orlando Expect From Security Partners
Change is hard because tickets, renewals, approvals, audits, and client commitments are already in motion. With 73% saying boards treat cybersecurity as a high business priority, the biggest tech companies in Orlando should expect security partners to work in good faith with incumbent IT providers, not force rip-and-replace decisions or create confusion over control ownership.
-
Clarify the scope: Ask what’s included, excluded, and available as a paid add-on before work starts.
-
Match controls to data: Require practical fluency in CMMC, HIPAA, GLBA, IRS, legal, or financial obligations.
-
Confirm operational ownership: Define who owns 24/7 SOC, EDR/XDR, SIEM, identity management, mobile security, and secure gateway tasks.
-
Review evidence cadence: Set expectations for evidence collection, dashboard reporting, access reviews, and POA&M updates.
A Practical Path For Biggest Tech Companies In Orlando
Cybersecurity priorities should connect to daily operations, compliance obligations, client trust, and measurable evidence, whether you’re protecting CUI, patient records, tax data, invoices, or remote access.
At Cyber Security Solutions, we’re a veteran-founded managed security and compliance firm headquartered in Tampa, founded by Horacio Maysonet, and we operate as both an MSP and MSSP while working with existing IT providers in good faith.
Contact us for a practical conversation about cybersecurity, compliance readiness, CMMC, NIST SP 800-171, HIPAA, managed security, 24/7 SOC, EDR/XDR, SIEM, identity management, secure gateway infrastructure, and continuous evidence collection. Security Ready. Compliance Ready. Always Ready.